<?xml version="1.0" encoding="utf-8"?><feed xmlns="http://www.w3.org/2005/Atom" ><generator uri="https://jekyllrb.com/" version="3.10.0">Jekyll</generator><link href="https://panagiotiscp.github.io/feed.xml" rel="self" type="application/atom+xml" /><link href="https://panagiotiscp.github.io/" rel="alternate" type="text/html" /><updated>2025-06-30T19:56:57+00:00</updated><id>https://panagiotiscp.github.io/feed.xml</id><title type="html">Your Name</title><subtitle>Web Developer from Somewhere</subtitle><entry><title type="html">CVE‑2024‑31026 – HTML Injection in GUnet Open eClass</title><link href="https://panagiotiscp.github.io/cve-2024-31026-html-injection/" rel="alternate" type="text/html" title="CVE‑2024‑31026 – HTML Injection in GUnet Open eClass" /><published>2024-03-24T00:00:00+00:00</published><updated>2024-03-24T00:00:00+00:00</updated><id>https://panagiotiscp.github.io/cve-2024-31026-html-injection</id><content type="html" xml:base="https://panagiotiscp.github.io/cve-2024-31026-html-injection/"><![CDATA[<p><strong>Date of Report:</strong> 24 / 3 / 2024</p>

<h3 id="description">Description</h3>
<p>GUnet Open eClass ≤ 3.15 is vulnerable to <strong>HTML injection</strong> via the chat input field inside any course module.</p>

<h3 id="impact">Impact</h3>
<p>Attackers can:</p>
<ul>
  <li>Inject deceptive content or phishing pages</li>
  <li>Auto‑redirect users to malicious sites</li>
  <li>Seed malware downloads</li>
</ul>

<h3 id="proof-of-concept">Proof of Concept</h3>
<p><a href="https://www.youtube.com/watch?v=-DwkPVmTrfY">https://www.youtube.com/watch?v=-DwkPVmTrfY</a></p>

<h3 id="affected-component">Affected Component</h3>
<p><code class="language-plaintext highlighter-rouge">chat</code> input field (<code class="language-plaintext highlighter-rouge">modules/chat/</code>).</p>

<h3 id="mitigation">Mitigation</h3>
<p>Escape or strip HTML, or render chat content with a whitelist sanitizer.</p>]]></content><author><name></name></author><category term="cve-2024-31026" /><category term="html-injection" /><category term="openeclass" /><category term="security" /><category term="gunet" /><summary type="html"><![CDATA[Date of Report: 24 / 3 / 2024]]></summary></entry><entry><title type="html">CVE‑2024‑31027 – Stored XSS via User Registration Fields</title><link href="https://panagiotiscp.github.io/cve-2024-31027-stored-xss-user-info/" rel="alternate" type="text/html" title="CVE‑2024‑31027 – Stored XSS via User Registration Fields" /><published>2024-03-24T00:00:00+00:00</published><updated>2024-03-24T00:00:00+00:00</updated><id>https://panagiotiscp.github.io/cve-2024-31027-stored-xss-user-info</id><content type="html" xml:base="https://panagiotiscp.github.io/cve-2024-31027-stored-xss-user-info/"><![CDATA[<p><strong>Date of Report:</strong> 24 / 3 / 2024</p>

<h3 id="description">Description</h3>
<p>Attackers can register accounts whose <strong>first name, last name, or username</strong> contain malicious scripts.<br />
These payloads execute later when admins search or list users.</p>

<h3 id="impact">Impact</h3>
<ul>
  <li>Admin session hijack &amp; privilege escalation</li>
  <li>System‑wide malware injection</li>
  <li>Data exfiltration</li>
</ul>

<h3 id="proof-of-concept">Proof of Concept</h3>
<p><a href="https://www.youtube.com/watch?v=7_0WgRv_sok">https://www.youtube.com/watch?v=7_0WgRv_sok</a></p>

<h3 id="affected-component">Affected Component</h3>
<p>User registration logic (<code class="language-plaintext highlighter-rouge">modules/auth/</code>).
Admin panel logic (<code class="language-plaintext highlighter-rouge">modules/admin/</code>).</p>

<h3 id="mitigation">Mitigation</h3>
<p>Sanitize/encode user attributes before storage and when rendering.</p>]]></content><author><name></name></author><category term="cve-2024-31027" /><category term="xss" /><category term="stored-xss" /><category term="openeclass" /><category term="security" /><category term="gunet" /><summary type="html"><![CDATA[Date of Report: 24 / 3 / 2024]]></summary></entry><entry><title type="html">You’re up and running!</title><link href="https://panagiotiscp.github.io/Hello-World/" rel="alternate" type="text/html" title="You’re up and running!" /><published>2014-03-03T00:00:00+00:00</published><updated>2014-03-03T00:00:00+00:00</updated><id>https://panagiotiscp.github.io/Hello-World</id><content type="html" xml:base="https://panagiotiscp.github.io/Hello-World/"><![CDATA[<p>Next you can update your site name, avatar and other options using the _config.yml file in the root of your repository (shown below).</p>

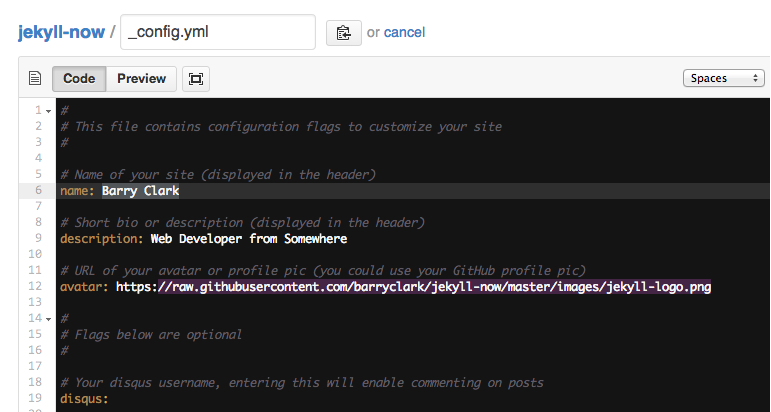
<p><img src="/images/config.png" alt="_config.yml" /></p>

<p>The easiest way to make your first post is to edit this one. Go into /_posts/ and update the Hello World markdown file. For more instructions head over to the <a href="https://github.com/barryclark/jekyll-now">Jekyll Now repository</a> on GitHub.</p>]]></content><author><name></name></author><summary type="html"><![CDATA[Next you can update your site name, avatar and other options using the _config.yml file in the root of your repository (shown below).]]></summary></entry></feed>